Do you ever get that sinking feeling, when you’ve forgotten the root password to your test lab? Again?
I hate it too! So I decided to figure out a way around it, using a work around…

Do you ever get that sinking feeling, when you’ve forgotten the root password to your test lab? Again?
I hate it too! So I decided to figure out a way around it, using a work around…
When setting up Active Directory delegation, you want administrators to be able to maintain Group Policy without being a Domain Admin.
If you read TechNet, Microsoft tells you to use Group Policy Creator Owners. However CO does not have permissions to modify or edit any other group policy objects.
Some administrators prefer to do everything manually, other automated. I have always preferred to have as much as possible automated or at least set up with a script so the action can easily be repeated without varying end results.
I have written a script which verifies that all users that should have a home folder has one, and that it has the appropriate permissions.

Security is very important, especially when it comes to IT.
We’ve created a password generating script to assist in making sure we all use high security passwords.
While you can perform granular assignments in Exchange 2010, there are also Predefined Role Groups that you can use if you want an easier way of assigning permissions to end users.

Today I ran into an issue with Internet Explorer on a Windows 2008 R2 server.
I have a GPO that pushes Local Intranet and Trusted sites but they would not be visible through the GUI in Internet Options.

A customer of ours asked us to look into making their environment more secure. However we noticed that they did not audit Group/User changes in their Active Directory, we adjusted this and here’s a quick guide how to deploy it in your corporation.

Yesterday I migrated our main file server to Windows Server 2012.
Noticed that Access-based enumeration was not working, I couldnt find the setting to re-enable it, or any good information on the web as to where it had gone.
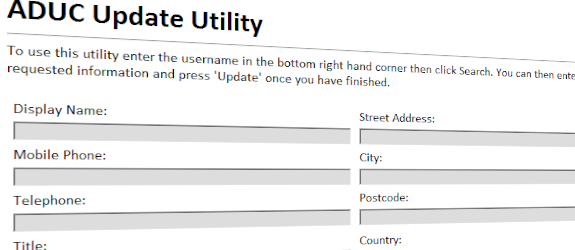
There might come a time where as a IT administrator you get tired of being asked to update peoples personal information in the Active Directory.
 Articles